DataStax
2025
Building a Scalable Account Hierarchy
Introduced a new enterprise layer to Astra DB, giving large teams centralized governance across users, billing, and deployments.

The Context
A product structure built for small teams, sold to enterprises.
Astra DB's organizational model was designed for a single tier that worked well for small, self-contained teams. But as DataStax pursued enterprise growth, that model became a ceiling. Customers managing 100+ engineers across dozens of databases were trying to fit complex, multi-department structures into a framework that offered no hierarchy above the organization level.
The Problem
Managing multiple teams in a tool designed for one.
We spoke with the admins and lead developers running these accounts. Three pain points came up in every conversation.
No centralized governance
Permissions had to be managed at each individual organization, with no way to set policy across teams from a single place.
Repetitive, tedious setup
Onboarding a new team meant repeating the same provisioning steps across each org — no inheritance, no templates, no shortcuts.
Structure that broke at scale
Managing 15–20 organizations with unique configurations under one account had no coherent framework.
The issue wasn't "managing more users"— it was the absence of a framework for grouping and governing multiple organizations under one unified view. No amount of UI polish would fix a structural gap in the product model itself.
The Defining Design Decision
Proposing a net-new layer: the enterprise tier.
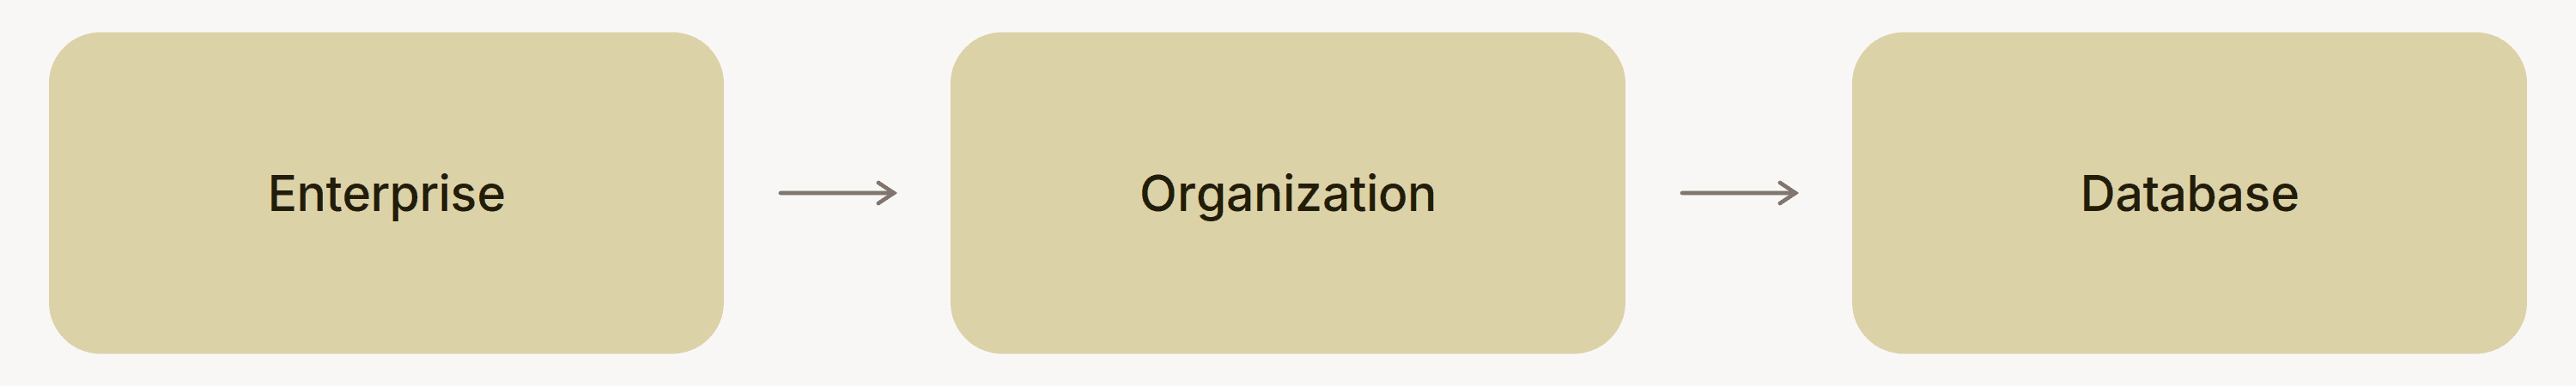
My core contribution was defining a new top-level entity in Astra DB's product architecture. I proposed introducing an enterprise layer that would sit above existing organizations, unifying them under a single governance structure without disrupting the flexibility individual developers depended on.
The Strategic Tension
Two explorations, one key learning.
We explored two distinct directions for organizing settings across the enterprise hierarchy: consolidating them in one panel or separating them by tier.
Option 1: Consolidated side navigation
Enterprise, organization, and personal settings lived together in one right-hand panel. Everything was in one place, but the panel got cluttered, and switching between accounts became harder, not easier.

Option 2: Dedicated settings
Settings separated contextually by tier, with account switching preserved in the main interface. Users could manage settings at any level without losing their orientation in the hierarchy.

Key learning
Consolidating settings did not simplify the hierarchy. Separating settings by tier, while preserving account switching in the main interface, gave users a clearer sense of where they were and what they could manage.
The Solution
A unified enterprise dashboard, built on the new hierarchy.
The final design gave enterprise admins a single place to govern everything — users, roles, billing, and database configurations — across all their organizations. From the enterprise tier, admins could set access policies that cascaded down, onboard new teams without repeating manual steps, and get a consolidated view of spend and usage without jumping between tabs.
01
Enterprise Overview
Every organization, along with its databases, members, and streams, is visible in a single view. Admins can see the full structure at a glance and move into any organization in one click, instead of switching between separate orgs.
02
Cascading policies
Policies like SSO, roles, and access permissions are set once at the enterprise level and apply automatically to every organization. Inside each org, inherited policies are marked so org admins know where a rule came from and that it can't be changed locally.
03
Streamlined onboarding
New organizations are created with enterprise settings already applied, including roles, permissions, and billing. Setup that previously took multiple steps now happens in a single flow.
04
Tier navigation
Users can switch between enterprises and organizations in a single click. Developers inside a single org see only what's relevant to them.
